Field-tested notes on robotics safety, ROS 2, embedded AI, AI agents, SaaS architecture and the practical systems that connect software to real-world outcomes.

Modular robot sensor boards on an I2C bus beside an oscilloscope

I2C Pull-Ups on Modular Robots: Check Every Sensor Configuration

A robot can pass its sensor checks with three breakout boards and fail with just one. Add two more boards and it can fail again, for a different electrical reason. Each module may bring both capacitance and another pair of pull-up resistors. Removing a module changes the circuit as surely as adding one.

Qualify I2C at the level of the supported assembly, separately for SDA and SCL. For every allowed combination, count the fitted pull-ups, bound the capacitance, and check both rise time and the current demanded from the weakest device pulling the line low. A clean trace from the fully populated prototype does not establish that the reduced configuration works.

The worked example below shows that failure pattern, then checks a different pull-up arrangement across all 31 nonempty combinations of five hypothetical boards. The calculations are executed synthetic examples, not measurements from a robot.

Server-side inspection holds a confidential response before releasing approved text to a browser

Streaming LLM Output: Put DLP Before the First Byte

A support assistant streams a case summary into a browser. Halfway through the answer, a data loss prevention scanner detects an internal identifier and replaces the message with a warning. The interface now looks clean. The identifier has already crossed the boundary: it may be in the network response, browser memory, a screen recording or a client-side telemetry event.

For an output channel that must not receive uninspected confidential text, hold model output on the server until the applicable inspection and authorization checks finish. A streaming model API can feed that buffer; it does not require the application to stream raw text to its user. Delayed detection can stop further disclosure, but cannot recall bytes already delivered.

The engineering decision is the unit of release: a whole answer, an independently authorized record, or a prefix that a narrowly defined detector can prove ready. Choose that unit before choosing the animation in the chat window.

Robot in a test cradle beside a CAN gateway, disconnected connector and diagnostic waveforms

CAN Bus-Off Recovery in Robots: Restart Without Replaying Motion

The CAN interface comes back. Telemetry starts moving again. A queued velocity command reaches a drive, and the robot resumes an action whose context disappeared during the outage. The interface recovery succeeded; the recovery procedure did not.

After CAN bus-off, restore communication with motion authority held closed. Invalidate commands from before the fault, establish fresh evidence from every required drive, reconcile their operating state, and require a new authorization to resume. A Linux interface reporting ERROR-ACTIVE is evidence about one CAN controller. It is not evidence that a wheel drive is ready, that a previous setpoint has been cleared, or that the robot should move.

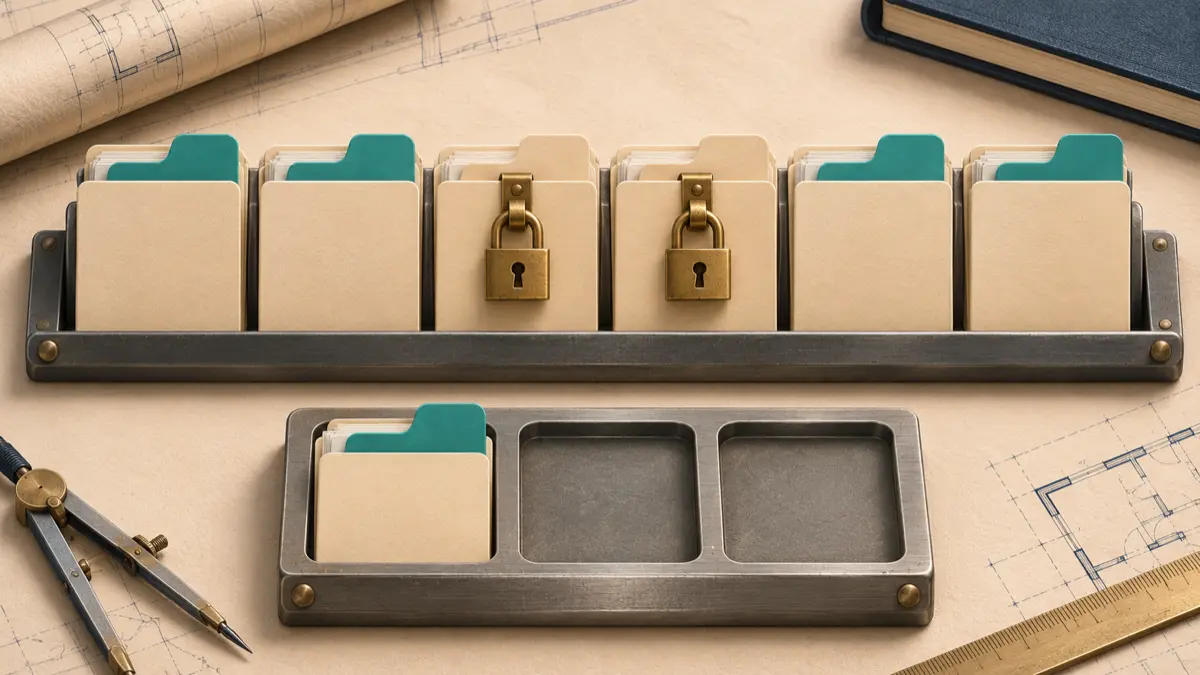
Locked and accessible document folders on a ranked file rail above a partly filled results tray

RAG Retrieval Tests for Permission-Filtered Vector Search

A support engineer asks an internal assistant how to restore a replica. The assistant cites one general runbook. A platform administrator asks the same question and gets three detailed procedures. Both answers look plausible. Before anyone changes the prompt or grants the engineer broader access, the search team needs to answer a smaller question. Which chunks, if any, should the engineer’s search have returned?

To test the vector retriever in a retrieval-augmented generation (RAG) system, build a reference result by scoring every eligible chunk for the same query and identity, then taking the nearest k. Compare the production result at the point where evidence leaves the trusted retrieval service. Count forbidden chunks, missing slots and missed neighbors separately. A retriever can fill every slot while missing the closest eligible procedure. It can also return one hit and be exactly right.

Robot wheel encoder connected to a microcontroller and a two-channel oscilloscope

Encoder Velocity Estimation: Why Low-Speed Robots Jitter

A robot creeps toward its docking station. The velocity loop runs at 1 kHz, but its encoder produces only about 130 counts per second. Most iterations report zero speed. An iteration that sees one count reports more than seven times the intended speed. The controller can end up reacting to the measurement staircase as well as the actual wheel motion.

Before retuning the PID, check how velocity is estimated. Count differences over a fixed window work well when that window contains enough counts. Timing the interval between encoder edges is often more useful at low speed, provided the estimate carries its age and becomes invalid on timeout, capture faults, or direction changes. Neither method turns a sparse position sensor into a continuously observed velocity sensor.

This article develops that choice for a wheel drive, with a reproducible numerical example. The calculations and Python experiment are synthetic; they are not measurements from a robot or a validated motor controller.

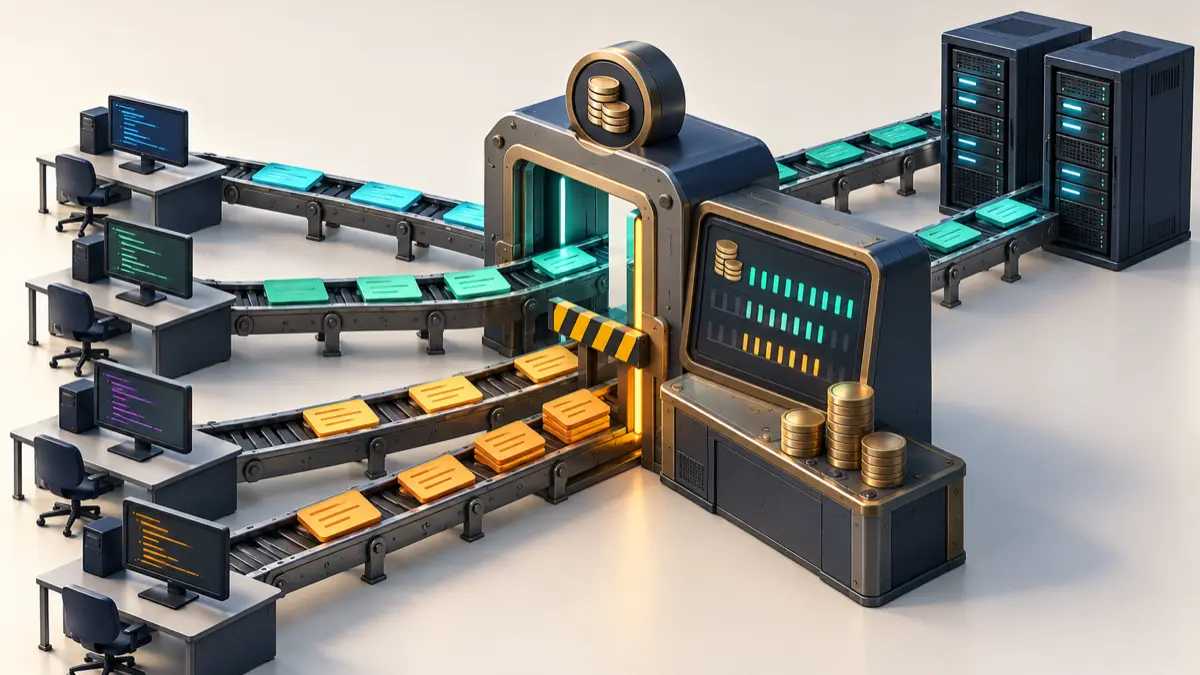
Parallel AI requests passing through a budget gate before reaching model servers

AI Agent Cost Budgets: Reserve Spend Before Parallel Work Starts

An enterprise agent has eighty cents left in its task budget. Twenty-four workers read that balance, each decide that a ten-cent request fits, and dispatch together. Every worker followed its local rule. The shared budget still failed.

The control has to happen before dispatch: reserve the maximum permitted cost of each attempt against a shared ledger, carry that reservation through uncertain outcomes, and settle it only when reliable usage evidence arrives. All child agents and retries must draw from the same accountable budget hierarchy.

That design can bound admitted variable spending, but only when requests have defensible cost ceilings and every spending path passes through the control. A dashboard, an average cost estimate, or a warning in the system prompt cannot provide that guarantee.

Isolated code execution with blocked networking and inspected output files

Sandboxing AI-Generated Code: Egress, Secrets, and Artifact Release

An enterprise assistant receives two confidential CSV exports and writes Python to reconcile them. The script runs in a fresh container, finishes successfully, and returns a report. That looks like a contained computation. It may also have downloaded a package, inherited a cloud credential, contacted an external endpoint, or embedded active content in the report.

None of those failures requires a kernel escape.

Treat agent-generated code as untrusted execution, with separate controls for what enters the sandbox, what it can reach, and what leaves it. The isolation runtime protects the host. Network policy, credential placement, resource limits, and artifact release determine whether the computation stays inside its business authority.

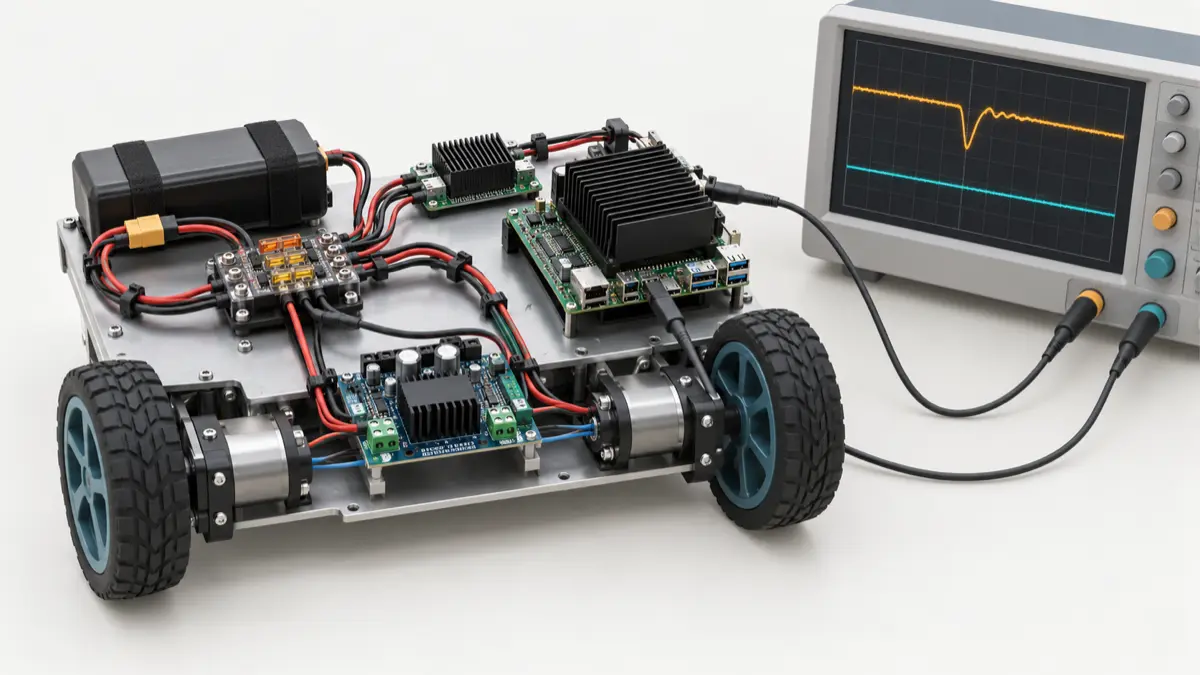
Robot power distribution and edge computer beside an oscilloscope showing a voltage dip

Robot Power Integrity: Debug Jetson Brownouts and Motor Transients

A robot runs its perception model correctly on the bench. Once the wheels accelerate, the camera disappears, inference latency jumps, or the Jetson reboots. The failure lands in the software team’s queue because that is where the symptoms are visible. Yet a new model, a ROS 2 QoS change, or a longer watchdog timeout cannot repair a collapsing supply rail.

To diagnose this class of failure, measure voltage at the consuming device while recording motor current, compute load and reset events. Separate sustained power demand from short load steps, and test braking as well as acceleration. A supply’s wattage rating alone does not establish whether the robot’s compute and sensor rails remain usable through those events.

The central engineering question is: can the electrical system preserve the operating conditions assumed by the AI and control software, including when several loads change together? The useful deliverable is a power-domain map with measured limits and a reproducible fault test, not just a larger battery.

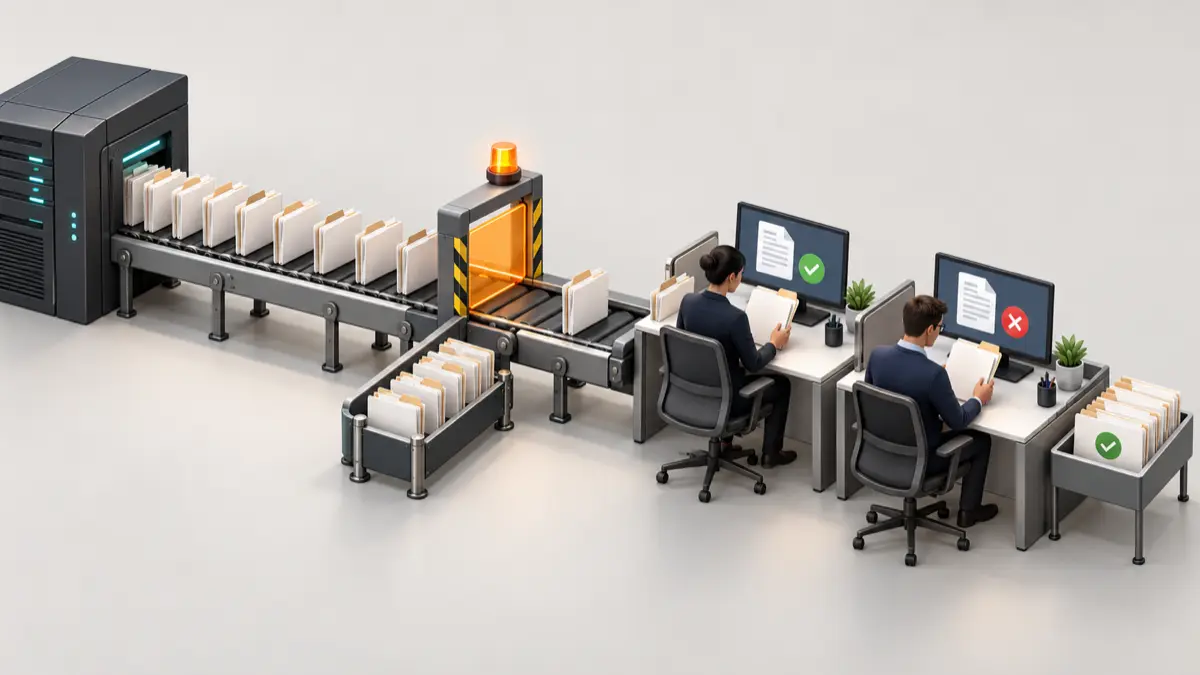
AI document queue metered through a gate to human review desks

Human Review Capacity for AI Workflows: Design Backpressure Before the Queue Grows

An AI service can process a thousand cases while the people responsible for its exceptions are still reviewing the first dozen. Model latency looks excellent. The workflow is getting slower.

Consider a support operation where an AI workflow proposes account adjustments. Most cases follow an approved, narrow automation path. Ambiguous evidence and higher-impact actions require human decisions. A change in incoming documents raises the exception rate from 5% to 8%. Nothing crashes, yet the same traffic now demands substantially more reviewer time. Scaling inference makes the problem worse.

Human review capacity must constrain how much work an AI workflow starts. Estimate the review minutes each case class creates, account for sampling and rework, and admit work against the capacity of qualified reviewers. When that capacity runs out, defer or reduce intake through a defined service path. Approval requirements remain in force.

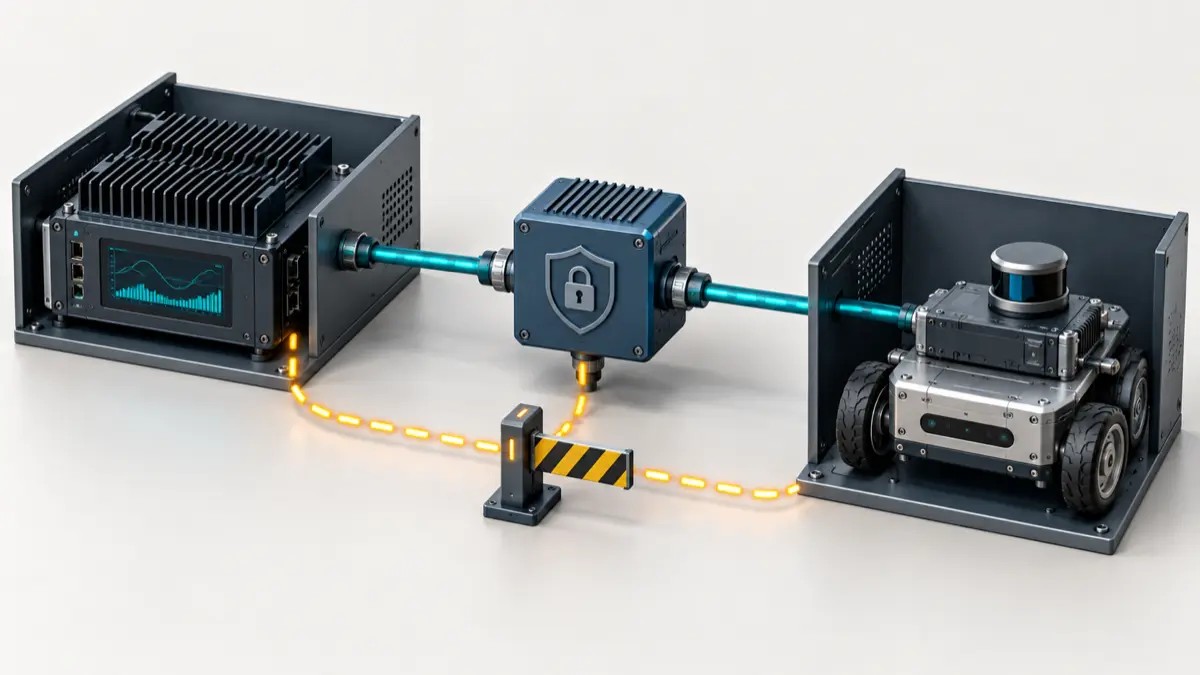
Separate AI and robot-control computers connected through a secured communication gateway

ROS 2 Security Enclaves: From Node Graph to Enforced Permissions

A robot copilot is allowed to read diagnostics and propose a docking task. The architecture diagram puts a command validator between the copilot and motion. Then someone gives both processes the same ROS 2 security credentials, or composes their nodes into one context. The diagram still shows a boundary. The deployed system may let the copilot publish directly to the controller.

ROS 2 security enclaves make that boundary enforceable at the middleware layer only when the credentials, process layout and permissions agree. Assign narrowly scoped identities to separate trust boundaries, generate permissions for the resolved communication graph, protect each identity’s private key, and test prohibited paths with the production deployment configuration.

The useful design question is specific: if the AI-facing process is compromised, which ROS interfaces can it actually use? A list of node names cannot answer it. An enclave-to-interface map, checked against the running system, can.